and it got me thinking... do I even want E2EE? For me, I will eventually use Joplin Server on my non internet facing server. It's powered down every night, and the OS is encrypted. So even if it's stolen, the data is encrypted by the OS encryption.
The question for me is about other devices like my tablets and phones. If those are stolen, what happens then? If someone tries enough pins (they are only 6 characters long and are just numbers after all), they have access to my device. Joplin stores all notes on those devices locally. Which basically means that if you have my device, you have my notes! E2EE wouldn't help in this case because Joplin doesn't ask for the encryption password when you open the app on those devices does it?
You can setup the mobile app to ask for your fingerprint when it starts. As for E2EE, it's up to you - it's another layer of security and maybe less necessary if you control both the device and server
Worth noting that when you use that, it also allows using the same pin used to unlock the phone to unlock Joplin too. But these days if you enter a few incorrect passcodes, the phone will have exponential backoff, so someone can't just try loads of passcodes continuously.
Personally I try to always use fingerprint to unlock my phone in public, because it's very easy for someone to look over your shoulder when you enter your pin, and then they can access any apps which use the 'system' biometrics like Joplin does. Whereas if you use your fingerprint and a thief steals your phone from your hand while it is unlocked, they won't be able to access anything which requires biometric re-entry.
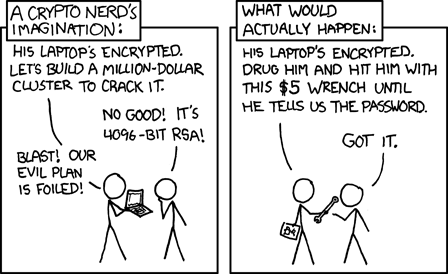
There's still a risk if you are co-erced to unlock your phone and specific apps by a thief at gunpoint, but then no security measure is safe if that's the case.
This isn't a philosophical question ;). I'm asking with respect to my specific setup I'm planning.
My additional research has put the portable device problem to bed. It turns out that tablets and phones although protected by short pins, these pins are hard to break because you only get 10-13 attempts at them. Then the device locks for good. The whole device is encrypted the moment you enable pins. So portable devices are a non issue from a data safety perspective. So it seems like I won't be using encryption after all since all my data is local and is encrypted by respective OS's.